The attacker is already inside the trust boundary.
Every significant breach in 2026 — the Cartrack 500GB exfiltration, the keyv supply chain attack affecting 600 million downloads, the autonomous AI agent breach of Australian government systems — shared one characteristic: the attacker operated inside protocols and applications the security stack was designed to trust.
ApexAegis closes that gap. Every sanctioned application, process, service and AI agent on a managed endpoint is issued a short-lived cryptographic token defining exactly which domains and protocols it is authorised to reach. Any network call outside that boundary is denied before it reaches the wire. A sanctioned application behaving outside its scope is treated identically to an unsanctioned process: access denied, session contained, forensic evidence preserved, user seamlessly moved to a clean workspace.
One control plane, nine enforcement layers.
Per-application cryptographic identity
RFC 8693 dual-token architecture binding every network call to the specific sanctioned process authorised to make it.
Built-in Identity Provider
Issues device certificates for mTLS and short-lived tokens for users, applications, processes, services and AI agents.
Built-in MDM
Device lifecycle management including remote wipe, OS and software management, and fleet-wide policy enforcement.
Continuous Adaptive Risk and Trust Assessment
Evaluates every network request in real time against process identity, behavioural signals and threat context.
Human vs. non-human intent differentiation
Distinguishes legitimate user-initiated network calls from programmatic or agentic calls at the kernel level.
Built-in ITSM with human-in-the-loop review
AI-assisted review of borderline access decisions, so exceptions reach your analysts instead of being silently auto-denied.
Remote Browser Isolation
Suspicious web traffic is rendered in a clean cloud session, without exposing the endpoint.
Just-in-Time Virtual Desktop
Provisioned from a verified clean snapshot when a threat is detected, so the user keeps working while the endpoint is isolated and evidence is preserved.
Fleet-wide MDM response
Halts updates across unaffected devices the moment a threat is confirmed on one endpoint.
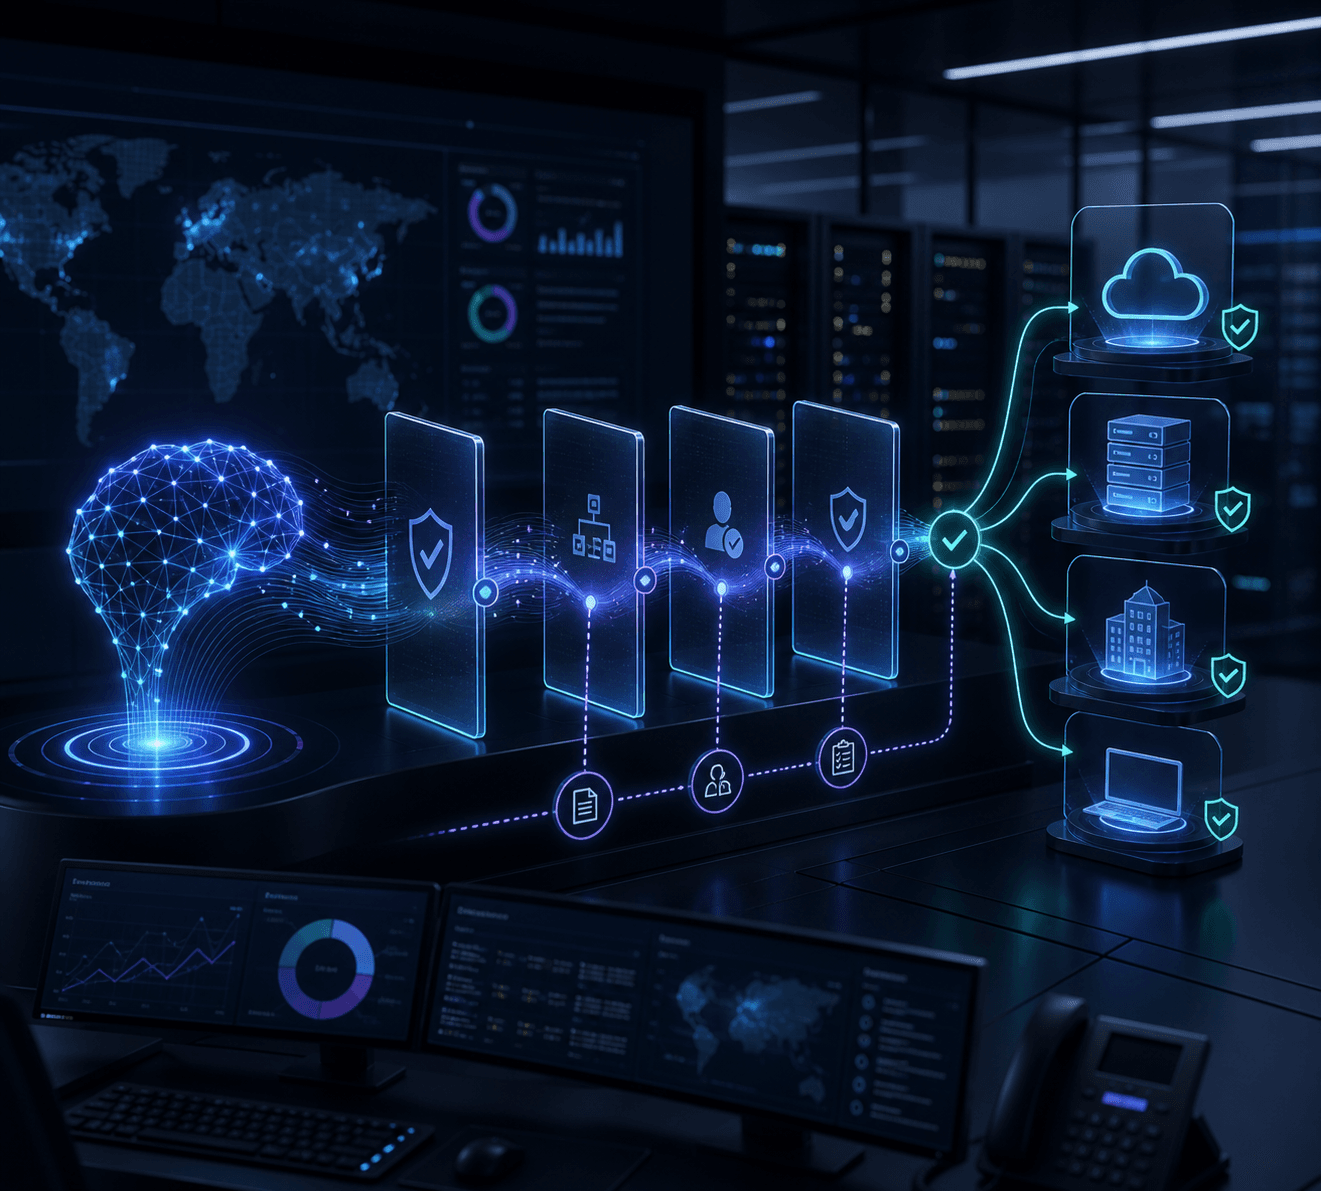
Every current SASE platform asks one question: is this user and device authorised?
ApexAegis asks a harder question: is this specific network call inside the scope this specific process was issued?
That second question stops supply chain attacks, process injection, rogue AI agents and shadow IT — categories every current platform misses, because the user and device are legitimate even when the process is not.
Production-grade.
ApexAegis is currently completing CREST penetration testing and compliance certification, with commercial delivery targeted for March 2027. We are inviting one or two design partners to run the platform in a pilot environment now, ahead of that date, to validate it in real enterprise environments and inform the final certification scope.